ARGOS: Designed for Consulting Companies
Deliver cloud security assessments with less manual work, consistent technical evidence and a report your client can act on.
ARGOS collects and analyses the environment and produces the deliverable. Your consultants spend their time on judgement, the client conversation and the remediation work that follows.
One engagement, start to finish
The structure of a cloud security assessment is the same for every client. ARGOS makes it repeatable without making it generic.
-
1
Scope
Agree the environments with the client: Azure subscriptions, the Entra ID tenant and Microsoft 365, AWS accounts.
-
2
Collect
Run a one-off scan with the client's own sign-in or a read-only role. Nothing is installed, and the credential is not kept after the scan.
-
3
Analyse
Review findings, attack paths and diagrams in ARGOS, with the evidence for each, and add your own judgement.
-
4
Deliver
Hand over the customer-focused report and walk the client through it. The remediation plan scopes the work that follows.
What changes for your team
- Repeatable
Repeatable delivery
Every client is assessed against the same rules and receives the same report structure, whoever on your team runs the engagement.
- Less manual
Less manual work
No scripts to maintain, no exports to stitch together and no diagrams to draw by hand. Collection, analysis and the first draft of the deliverable are automated.
- Evidence
Consistent technical evidence
Each finding carries the configuration it rests on, and each attack path step carries its proof, so a conclusion can be checked rather than taken on trust.
- Report
Customer-ready reports
An executive summary, priority risks, attack path examples, a remediation plan and timeline, and compliance by environment, downloaded from the dashboard.
- Follow-on
Assessment and remediation engagements
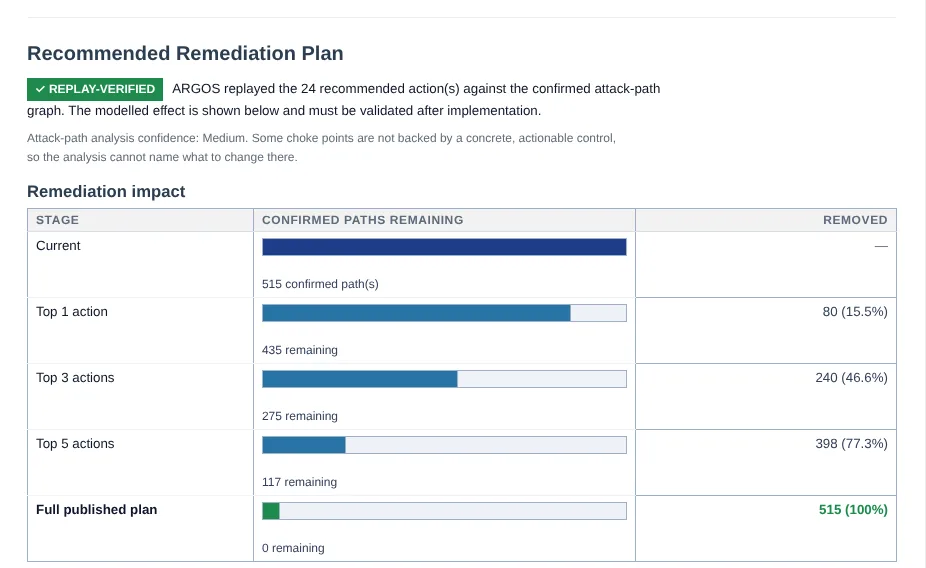
The remediation plan names the changes that close the most attack paths, which makes it straightforward to scope the next piece of work and to reassess once it is done.
What your client receives
A customer-focused assessment report, delivered as a single ZIP from the ARGOS dashboard, with links back into ARGOS for the full technical evidence.
- 01
Executive summary
- 02
Priority risks
- 03
Attack path examples, with their confidence
- 04
Recommended remediation plan and timeline
- 05
Compliance by environment
- 06
Azure network and architecture summary
See an assessment from your client's side
Book a walkthrough and we will run through an assessment and the report it produces.