Work across customer environments
One ARGOS account holds every customer's connections. Reader, Contributor and Cloud Admin roles see only the connections assigned to them, so each engineer stays inside their own customers.
 ARGOSCloud Security
Assess your customers' Azure, Entra ID, Microsoft 365 and AWS environments without agents. Identify real attack paths, verify exposure and deliver customer-ready reports without building your own assessment tooling.
Built for MSPs, MSSPs and cloud consultancies.
MSPs often take responsibility for customer environments without a complete understanding of privileged access, application permissions, exposure, Conditional Access gaps or attack paths. ARGOS gives you that visibility before the risk becomes yours, and supports every stage of the engagement that follows.
Connect with agentless, read-only access and produce a baseline of the customer's environment: findings, attack paths, diagrams and a report. A baseline you can charge for.
Turn prioritised findings and the remediation plan into scoped improvement work for your team. Where your plan includes remediation and the customer grants write access, selected fixes can be applied from ARGOS.
Scan again once the work is done to show the customer what it closed and what still needs attention.
Connect the environment for daily scans, with new findings sent to Slack, Microsoft Teams, Microsoft Sentinel or Jira. Recurring assurance, and recurring revenue.
One assessment can lead to remediation work, recurring assurance and a stronger customer relationship.
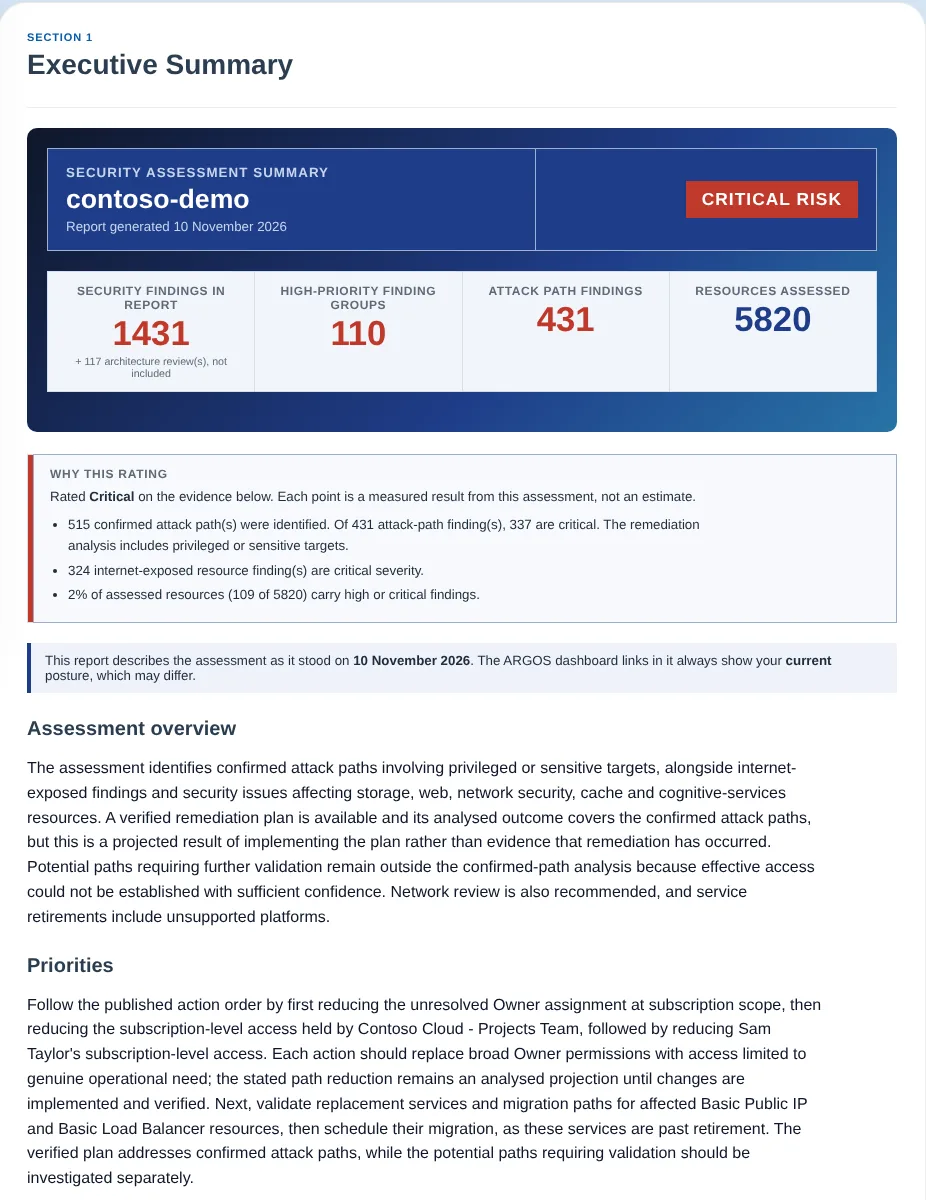
Each assessment produces a customer-focused report, downloaded from the ARGOS dashboard as a single ZIP by anyone authorised for that customer's environment. It is written to be handed over without rewriting, and links back into ARGOS for the full technical evidence.
Configuration baselines tell you what is misconfigured. These tell you what an attacker could do with it.
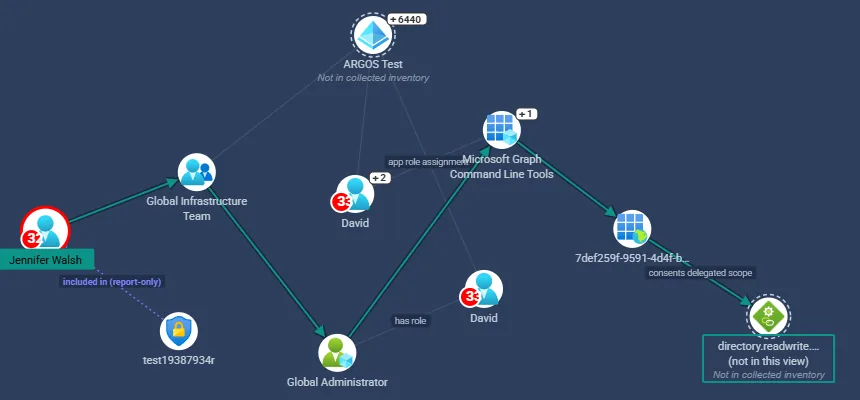
Show how identities, applications, permissions and cloud resources combine into meaningful risk.
Automatically visualise customer environments and the relationships between resources.
Identify users, applications and scenarios that fall outside intended policy coverage. How it works
Actively test whether supported Azure resources are genuinely reachable, rather than merely configured as public, and analyse the full network path for AWS EC2.
Reachable Not reachable
Understand what identities can actually reach or control across the environment.
Generate structured reports with findings, evidence, diagrams and remediation guidance.
The same assessment, run the same way, for every customer you look after.
One ARGOS account holds every customer's connections. Reader, Contributor and Cloud Admin roles see only the connections assigned to them, so each engineer stays inside their own customers.
Every customer is assessed against the same rules and gets the same report structure. A one-off scan uses a sign-in or token that is held only for the scan and never stored on the customer record.
A report the customer can read and act on, generated from the dashboard whenever you need it, with no slide deck to assemble.
Connected environments are scanned daily. New findings reach the tools your team already works in: Slack, Microsoft Teams, Microsoft Sentinel or Jira, with ServiceNow incidents created from a finding on demand.
Every user has an API key. Start one-off scans, read findings and inventory, and add or remove customer environments from your own automation. About the API
Attack paths with the evidence for each step, ARGOS AI explanations of each finding in context, and a remediation plan that names the changes closing the most paths.
As an MSP, we support mid-sized companies and hospitals with complex Microsoft and cloud infrastructures. ARGOS Cloud Security is the ideal tool for us to efficiently and scalably integrate automated security assessments into our consulting portfolio. ARGOS is a core part of our approach, both for initial audits and ongoing monitoring.
Der Azure Security Scan war schnell und unkompliziert durchgeführt und hat uns dabei geholfen, Sicherheitslücken zu schließen und unsere Security Konfiguration zu optimieren. Dadurch wurde unsere Konfiguration deutlich robuster. Vielen Dank dafür!
Sebastian Wondrak
IT Security Architect
German original
ARGOS has proven to be an invaluable asset for our consulting team. Its robust features and user-friendly interface have made a significant impact, providing super useful insights and aiding us immensely in addressing cloud security concerns during cloud security assessments.Microsoft Security MVP
Tell us a little about your current services and we will show you how ARGOS can support customer assessments, remediation and ongoing assurance.